Which laws, which parts
Your markets decide the laws, and what’s in scope.
Find out whether your store handles personal data the way GDPR, UK GDPR and US state laws expect, with every gap ranked by risk in a fix plan.

Adobe Commerce gold partner
#1 Adobe Commerce partner worldwide
Hyvä Platinum Partner
40+ projects delivered
ISO certification
9001 & 27001
Most certified Hyvä agency worldwide
200+ Adobe Commerce Certifications
Award-winning agency
3× eCommerce excellence award
We work out which laws apply, test the store against them, and give you a fix plan your team can run.
Cookie consent before any tracking tag
A privacy notice that matches the store
Access and deletion requests, end to end
US opt-out of sale and sharing
Data kept only as long as needed
Your markets decide the laws, and what’s in scope.
What loads before consent, and where deletions end up.
Every gap ranked by risk and effort, with the Magento fix.
We’re engineers, not lawyers. The plan is technical, and legal sign-off stays with your counsel.
An extension switches on a feature. It’s a reasonable first step, but it doesn’t tell you the things a regulator or a customer asks.
Pixels and analytics loading before the visitor consents.
Extensions and integrations sending it to third parties.
The ERP, the email platform, backups, and how long anything is kept.
Across every tool that shares a visitor’s data.
Where your customers are decides it, not where your company is registered.

Apply when you sell to people in the EU or the UK, with consent before non-essential cookies, a lawful basis for each use of data, and data kept no longer than needed.
California residents can know, delete and opt out of the sale or sharing of their data. Other states have similar laws, each with its own thresholds.

A US store selling into Europe falls under GDPR for those customers, and a European store selling to Californians may fall under California’s law.
It’s spread further than most teams expect, and you can’t honor a request for data you don’t know you hold.
Names, addresses and saved payment tokens.
Including guest orders and their addresses.
Often kept indefinitely, with contact details.
Newsletter sign-ups and their consent records.
Tied to a customer’s name and account.
Server and payment logs with emails or IPs.
Staff accounts and their activity records.
In your ERP, email, analytics and backups.

The audit maps each of these before anything else.
So an access or deletion request reaches every place the data sits.
Consent is a technical test. Open the store in a clean browser, don’t click anything, and see what loads.
Outside the consent tool’s control.
With consent checks missing from individual tags.
Unaware of the consent setting.
Magento’s cookie restriction mode only holds back its own cookies, not your tag manager or extensions.
Some extensions send customer data as part of their job. Others do it as a side effect, through tracking code nobody remembers adding.
With what each sends, and where it goes.
The one your privacy notice and contracts should reflect.
Some no longer earn their place on the store.
When a customer asks for their data or its deletion, the request has to reach every system that holds it.
Producing everything you hold on one customer, across Magento and every system it feeds.

Customer account, orders and quotes
Newsletter and consent records
Copies held in the ERP, email platform and analytics
A Magento deletion doesn’t reach every system, and some records must stay for tax.
Removed from Magento, the email platform and analytics
Orders kept where the law requires, and nothing else
Backups handled by a documented rule
A US customer’s opt-out of sale or sharing has to reach every tool that shares their data.
Advertising and analytics tags respect the opt-out
Browser-level signals checked where they apply
The opt-out recorded, so it survives the next visit
Most Magento stores keep everything forever, because nothing was ever set to clear it.
How long orders, accounts, quotes and logs are kept
Automatic clean-up where Magento allows it
Rules your counsel can review and approve
Three steps, each ending in a document you keep.
Which laws apply, and which extensions are in scope.
 A scope summary
What loads before consent, and where data goes.
 A written audit report
Each gap ranked by risk, with the change that closes it.
 A plan your team can run

Legal interpretation stays with your counsel, and the plan is written so they can review it.
If you’d like us to make the changes, we can, with the consent platform you’ve already chosen.
Tracked in the Magebit Client Portal, with every fix reviewed by a developer.
For larger programs, a team that works alongside your own roadmap.
The clean-browser test again: whatever is installed, nothing loads before consent.
Writing your privacy policy is for your lawyer. Keeping the fixes in place after every release is for us.
Magebit brings Magento expertise to businesses in every country. From Perth, Melbourne and Sydney to London, Dubai, New York, Los Angeles, Charlotte and Florida, we’re ready to help wherever you are.

The top-ranked Adobe Commerce agency on the planet by Adobe themselves.


The most certified Hyvä agency in the world. Confirmed by Hyvä themselves, twice.
Explore Hyvä development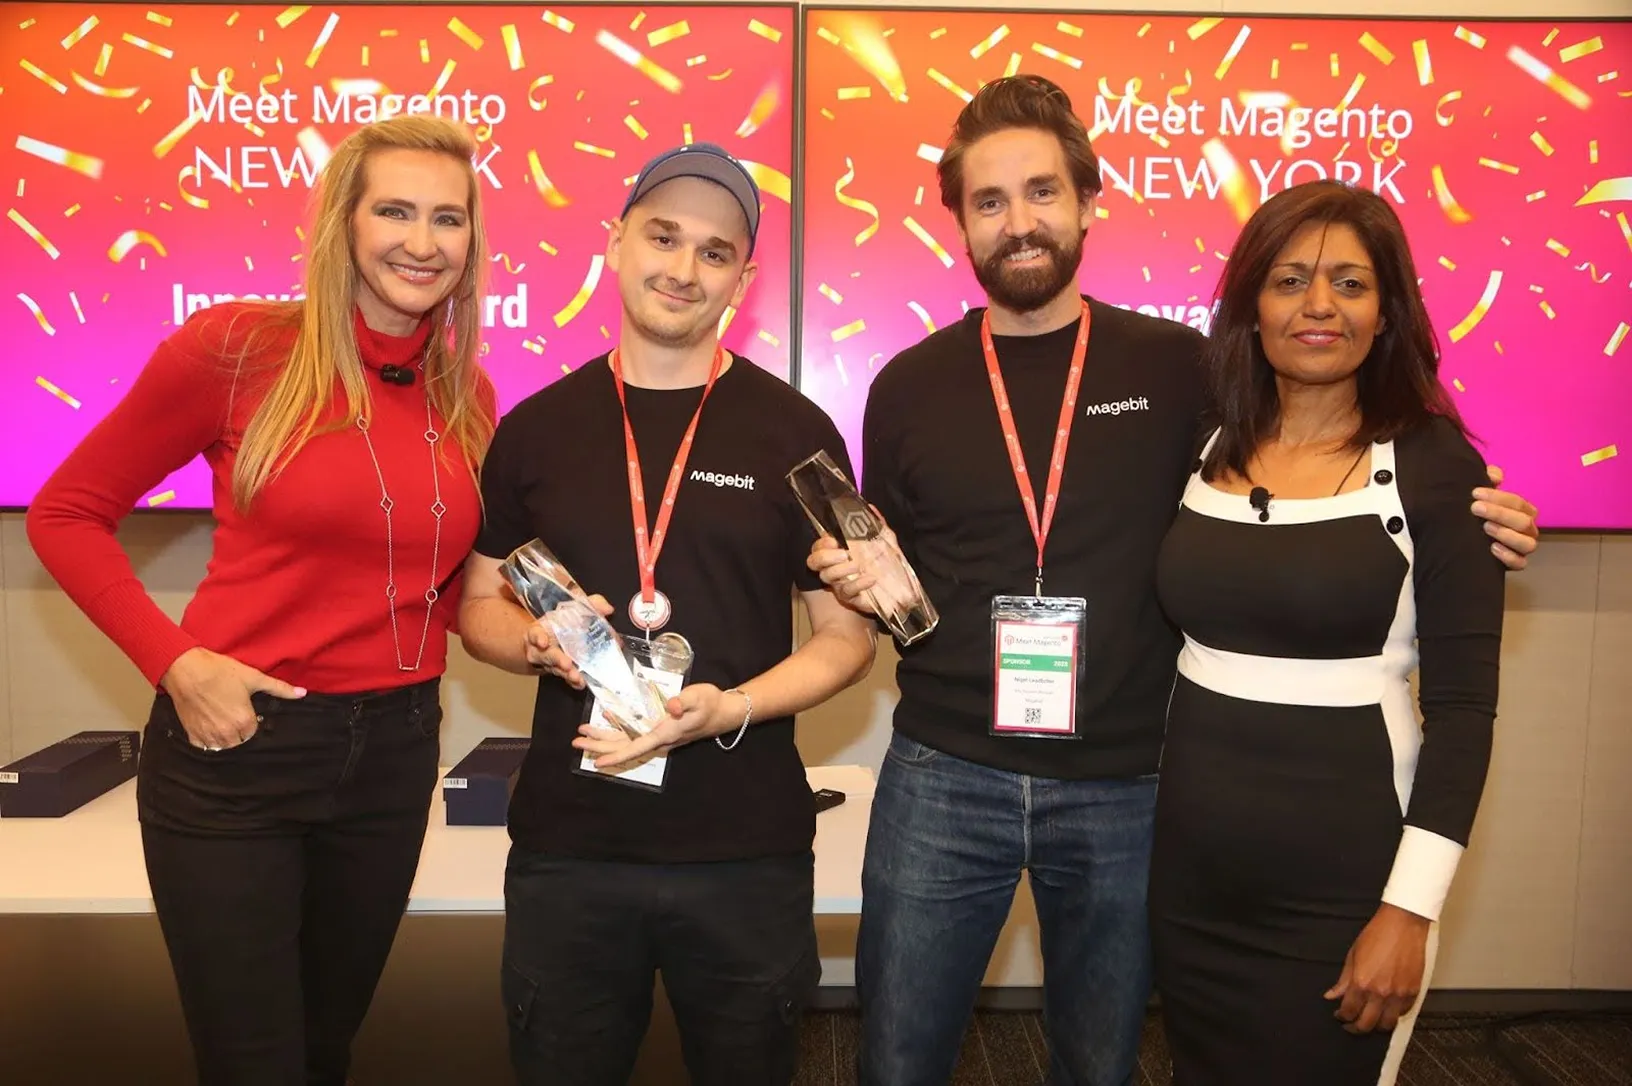
Innovator, World Traveler, and eCommerce Excellence awards across Meet Magento NYC and HIVE London, and more.
The most-certified Hyvä agency worldwide and the first Hyvä Platinum Partner in the USA. 55+ Hyvä certifications and 40+ projects delivered.
ISO 9001 & 27001 for quality and security.
Truly agile team that moves and adapts faster than your typical agency.
UX grounded in large-scale ecommerce research.
Most stores we look at have a consent banner and tags firing behind it. Tell me where your customers are and what runs on your store, and we’ll show you what’s actually happening to their data.
Reviewed by Kristaps Rjabovs
Co-founder of Magebit, Forbes 30 Under 30
If you can’t find the answer you’re looking for, feel free to reach out to us. We’re here to help.
No platform is compliant on its own, because compliance depends on how the store is configured and what runs on it. Magento includes a basic cookie restriction mode, but it doesn’t control third-party tags, handle data requests across your other systems, or manage retention.
Not necessarily. An extension adds features such as a consent banner or data export. It doesn’t confirm that tags are blocked before consent, that deletion reaches your other systems, or that your extensions aren’t sending data elsewhere. The audit checks those.
Whichever fits your stack and your markets. The important part is testing that it actually blocks tags until the visitor consents, which is the first thing we check.
It can, if you sell to California residents and meet its thresholds. We work out which US state laws are likely to apply during the consult, and your counsel confirms it.
Possibly. Virginia, Colorado, Utah, Connecticut, Texas and other states have their own laws, each with its own thresholds. The consult maps where your customers are against them.
It depends on the extension. The audit lists every extension and script that handles personal data, what it sends and where, so you can decide what to keep, configure or remove.
It has to reach every system that holds their data, not just Magento, while keeping the records you’re legally required to retain. We map how requests flow today and what needs to change.
No. We’re Magento engineers. We find the technical gaps and fix them; your counsel handles legal interpretation and sign-off.
Explore the Magento services Magebit has to offer.
Tell us where your customers are and what runs on your store. We’ll start with a short consult.
Which laws apply, and what’s in scope.
Consent, trackers, requests and retention.
Every gap ranked by risk, yours to keep.
We use cookies to understand visits, show relevant ads and play videos. You choose what to allow.