Magento security patches and hardening
Adobe's security patches assessed, tested on staging and released to your store on schedule, with the hardening that keeps the next attack out.

Adobe Commerce gold partner
#1 Adobe Commerce partner worldwide
Hyvä Platinum Partner
40+ projects delivered
ISO certification
9001 & 27001
Most certified Hyvä agency worldwide
200+ Adobe Commerce Certifications
Award-winning agency
3× eCommerce excellence award
How far behind is your store?
Most stores we take on are several patches behind, and nobody can say exactly how many. That’s the first thing we find out.

Patches outstanding
Every security and isolated patch your version should have, checked against what’s installed.
How long each has been open
Because a known flaw left open for months is what automated attacks look for.
What’s blocking them
Extensions and custom code that stop a patch applying cleanly.
How a patch reaches your store: assess, test, release
A patch applied straight to production is how a security fix becomes an outage.
 Assess
What the patch changes, and whether it touches your extensions or custom code.
 Test
Applied on staging and checked through browsing, cart, checkout and the admin.
 Release
Reviewed by a certified developer, then released outside your busiest hours.
Security patches, isolated patches and quality patches
Adobe ships three kinds of fix. Treating them as one is how stores end up exposed or over-patched.
Security patches
Adobe’s scheduled releases of security fixes. Every one is assessed, tested and applied, with no exceptions.

Isolated patches
A single urgent fix released between versions, usually for a flaw that’s being exploited.
Quality Patches Tool
Optional fixes for specific bugs, applied when your store is affected and left out when it isn’t.
Clearing a patch backlog
When a store has drifted, patches are cleared in order of risk, not in the order Adobe released them, then kept on schedule.
- Week 1Internet-facing flaws
- Week 2Blocking extensions
- Week 3Remaining patches
- ThenMonthly, on schedule
Hardening beyond patches
Patches close known flaws. Hardening closes the doors attackers try first, whether or not a patch exists yet.
A firewall in front of Magento
Cloudflare or AWS WAF stops attacks at the edge, before a request ever reaches the store.
- WAF rules tuned for Magento’s admin, checkout and APIs
- Bot management and rate limiting on login and checkout
- DDoS protection and caching at the edge
An admin that’s hard to reach
Most break-ins start with an admin login. These make it the hardest door to open.
- A custom admin path, limited to known IP addresses
- Two-factor authentication for every admin user
- No shared accounts, and access removed when people leave
Checkout protected from skimmers
Card skimmers hide in injected JavaScript. Checkout is locked down so only approved scripts run.
- Content Security Policy limiting which scripts can load
- Subresource integrity on third-party scripts
- Monitoring for new or changed scripts on payment pages
Fewer extensions, all of them current
Every extension is code someone else wrote running inside your store. Fewer is safer.
- Unused extensions removed
- The rest kept current and checked for known flaws
- Abandoned modules replaced before they become a risk
A server with nothing left open
The store is only as secure as what it runs on, so the server gets the same review.
- File permissions and ownership corrected
- PHP, database and search engine kept on supported versions
- Unused services closed, and backups held off the server


When a patch is not enough
Patches only reach versions Adobe still supports. Once yours falls out of support, the fix is an upgrade, not another patch.
Magento version upgradesWhere patching ends
When Adobe stops releasing patches for your version.
Where an upgrade begins
Moving to a supported version, with extensions checked for compatibility first.
Patching and PCI compliance
Keeping software patched is part of PCI DSS, and an assessor will ask for proof that it happened.
Evidence kept for every patch
What was applied, when it was tested, and who released it.
A named developer on each release
So the record holds up when someone checks it.
When the store is already compromised
A patch stops the next attack, not one that’s already happened. A compromised store needs cleaning before it’s patched.
Contained and cleaned
Injected code, rogue admin users and backdoors found and removed.
The way in closed
The flaw that let the attacker in patched, so they can’t return the same way.
Watched afterwards
Monitoring for signs the attacker is trying again.
Two ways we deliver it
Patching runs inside our support system, or inside a team that works on your store every week.
Patching through SOLVE
SOLVE, our Structured Operations for Live Ecommerce, runs patching as part of the support plan, tracked in the Magebit Client Portal.

Every patch logged in the Portal, with its status
AI assists; a developer reviews every release
Estimated and approved before work starts
Patching inside a dedicated team
If you already have a dedicated Magento team with us, patching is part of the team’s week, alongside the roadmap.
The developers who know your code apply the patch
Scheduled around your releases and campaigns
No separate ticket or contract
Live stores we keep patched and secure
Security work isn’t a one-off for us. These stores are patched, hardened and supported by the same team, year after year.
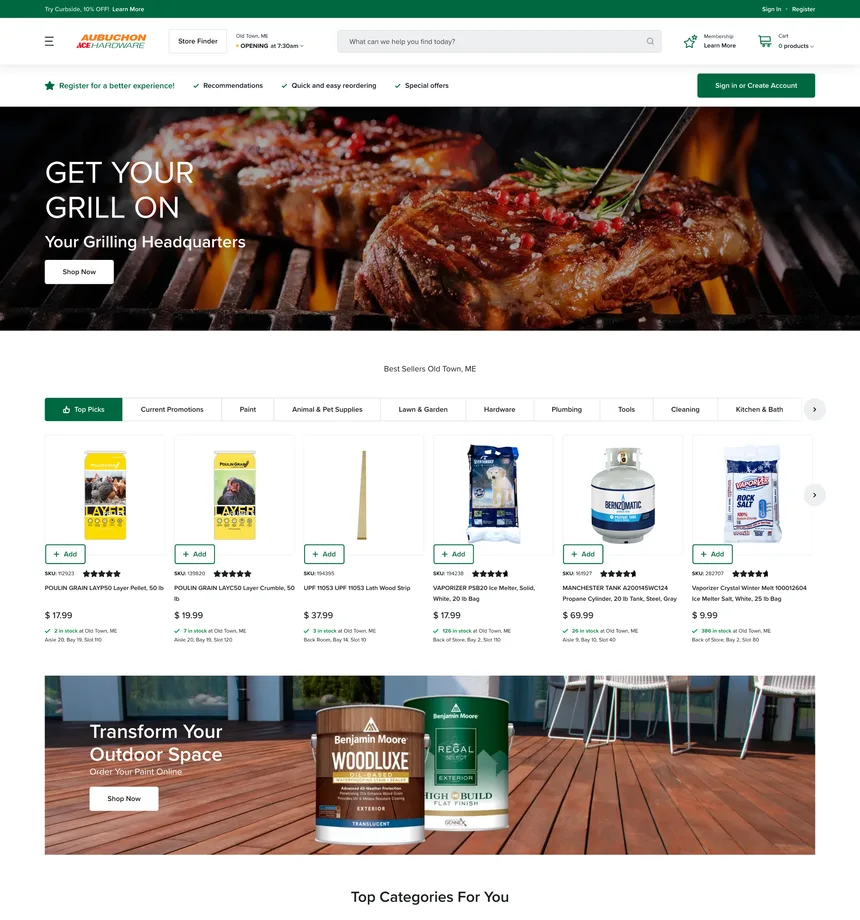
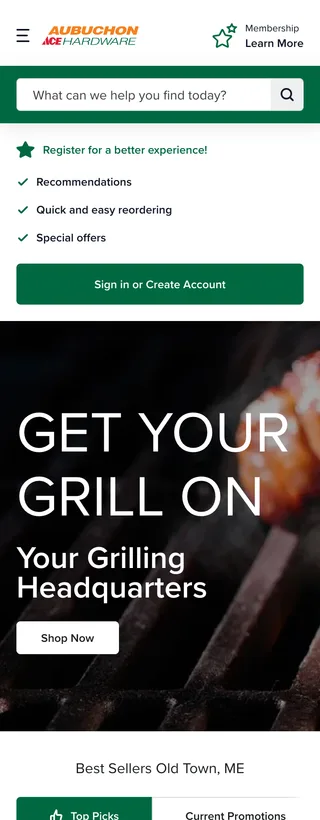
America's neighborhood hardware stores, online
- Support and security services for a 100+ store network
- Store pickup, store finder and rewards kept reliable at scale
- Continuous Core Web Vitals and SEO programme



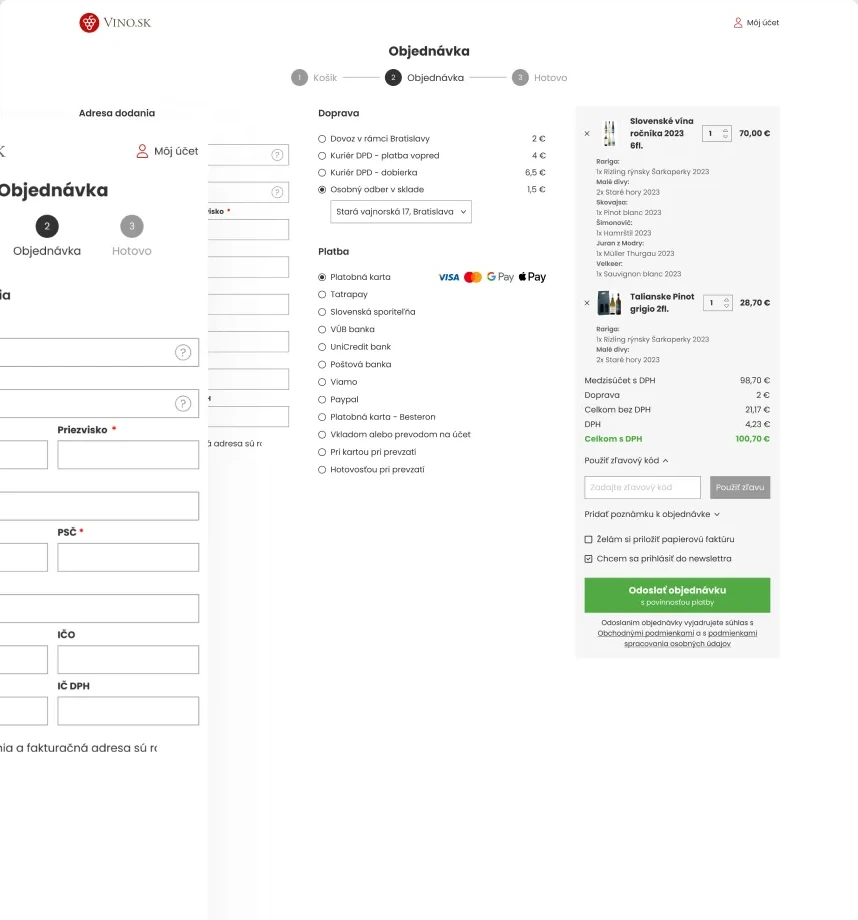
A Slovak wine retailer, supported for years
- Checkout, search and analytics tuned over years of iteration
- Security hardening and age-gated flows kept compliant
- The same team, year after year, knowing the store inside out

The Baltic stores of a global beauty icon, supported end to end.
- Ongoing support across Latvia, Lithuania and Estonia
- Multilingual SEO and content programme alongside maintenance
- One-step checkout, store pickup and local payments


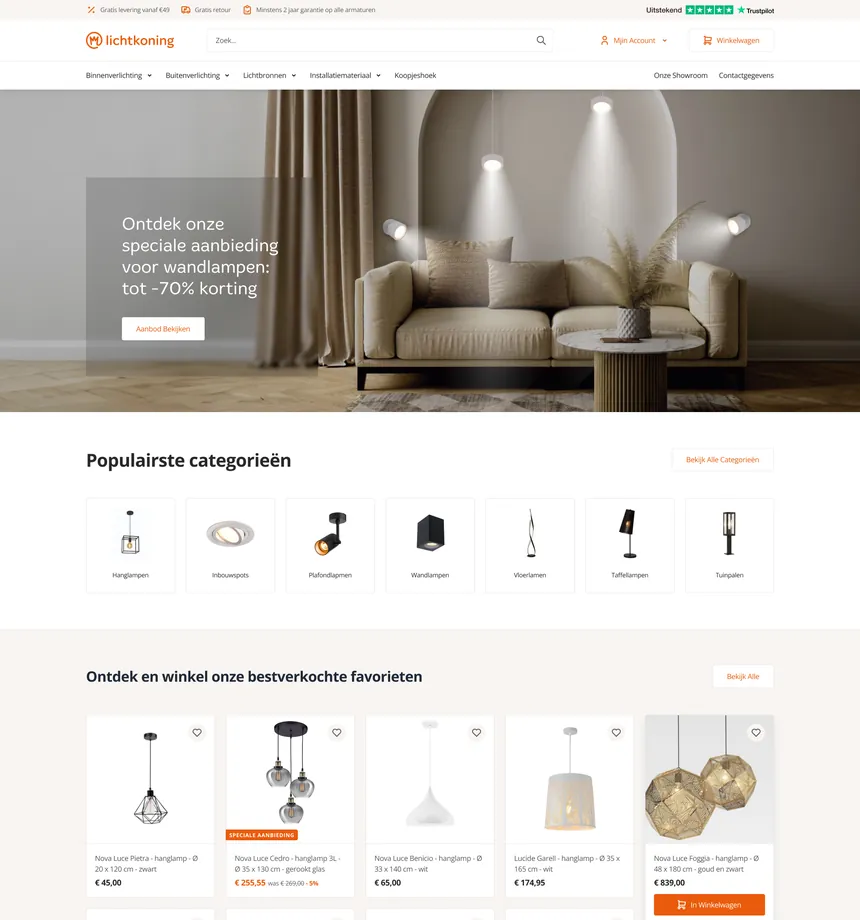
A Belgian lighting retailer, from old Magento 2 to a fresh Hyvä build
- Supported for years, then rebuilt on Hyvä, live February 2026
- Three countries under local brand names, one platform
- Proof that long-term support and modernization are one path


Why ambitious brands choose Magebit
Magebit brings Magento expertise to businesses in every country. From Perth, Melbourne and Sydney to London, Dubai, New York, Los Angeles, Charlotte and Florida, we’re ready to help wherever you are.

#1 Adobe Commerce partner worldwide
The top-ranked Adobe Commerce agency on the planet by Adobe themselves.


55+ Hyvä Certificates
The most certified Hyvä agency in the world. Confirmed by Hyvä themselves, twice.
Explore Hyvä development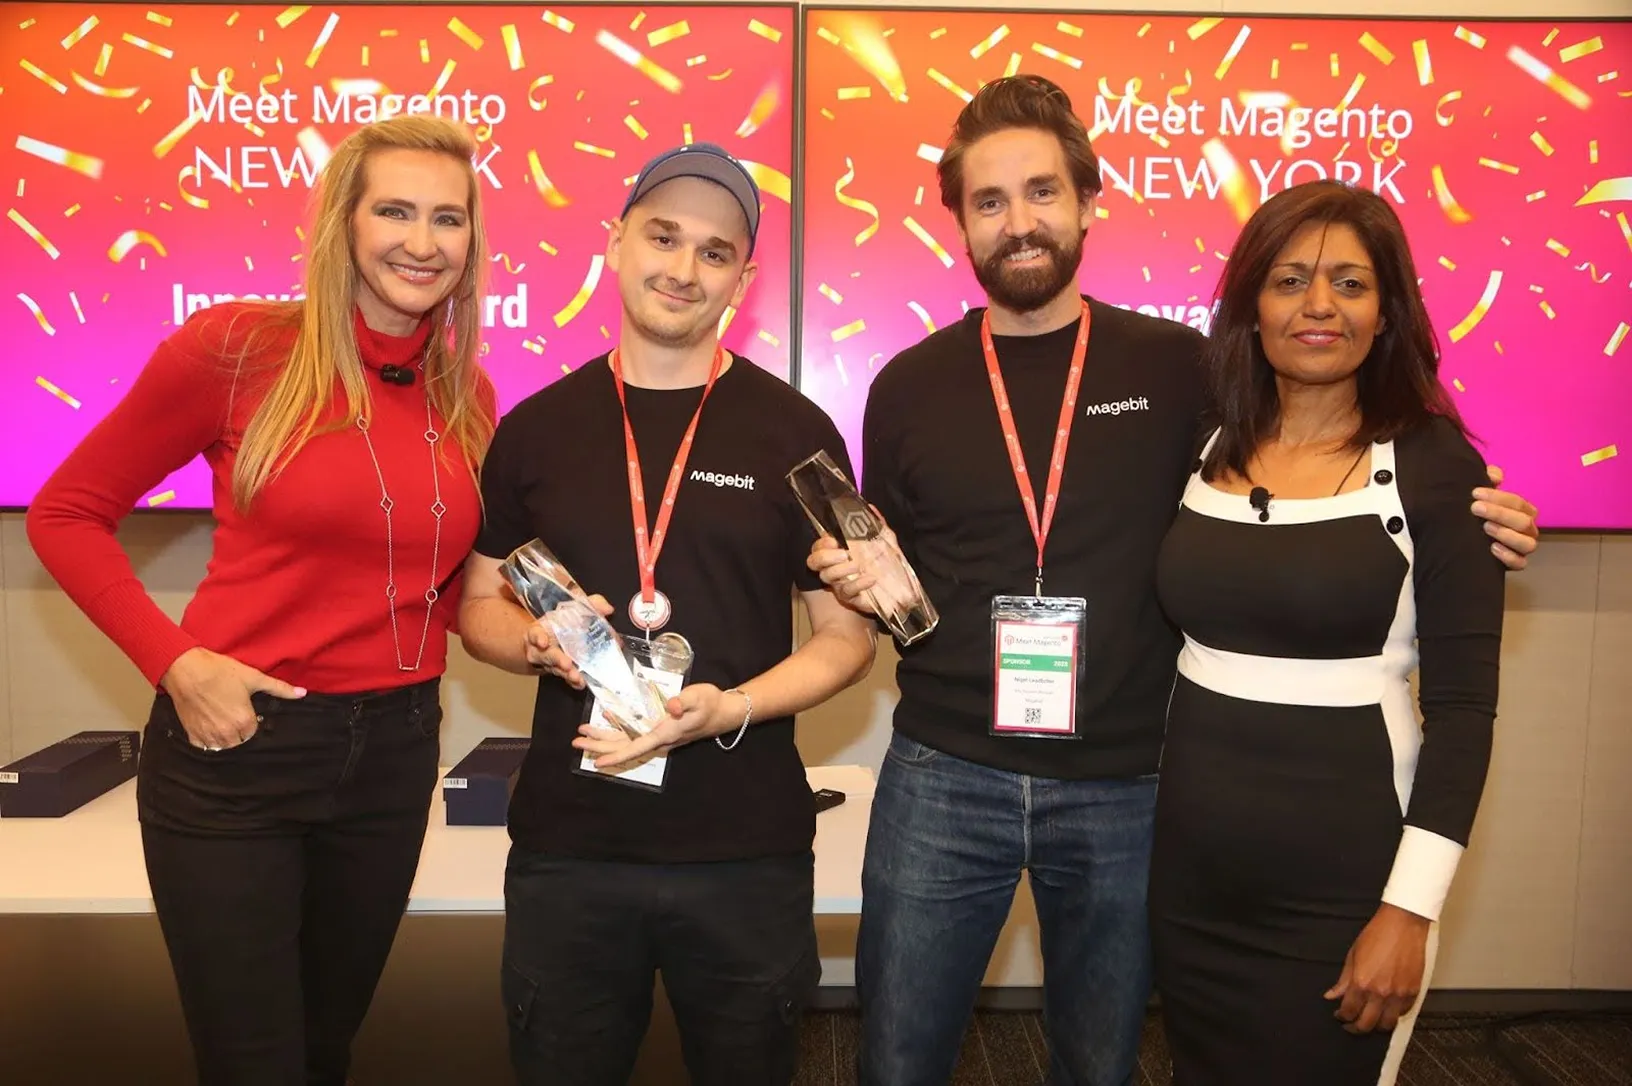
Award-winning solutions
Innovator, World Traveler, and eCommerce Excellence awards across Meet Magento NYC and HIVE London, and more.
Hyvä Platinum Partner
The most-certified Hyvä agency worldwide and the first Hyvä Platinum Partner in the USA. 55+ Hyvä certifications and 40+ projects delivered.
ISO certified
ISO 9001 & 27001 for quality and security.
Scrum Alliance certified team
Truly agile team that moves and adapts faster than your typical agency.
Baymard certified design team
UX grounded in large-scale ecommerce research.
Find out how far behind you are
Most stores that come to us after an attack were a few patches behind and didn’t know it. Send me your store and we’ll tell you exactly what’s outstanding, what’s blocking it, and the order we’d clear it in.
Reviewed by Kristaps Rjabovs
Co-founder of Magebit, Forbes 30 Under 30
Frequently asked questions
If you can't find the answer you're looking for, feel free to reach out to us. We're here to help.
Compare the patches your version should have against what’s installed, including isolated patches released between versions. A patch-status check does this for you and also shows which extensions are blocking patches.
Security patches are Adobe’s scheduled security releases. An isolated patch is a single urgent fix Adobe publishes between those releases, usually for a flaw that’s being exploited.
No. Those are optional fixes for specific bugs, so we apply them only where your store is affected, rather than adding code that changes nothing for you.
That’s what testing is for. Every patch is applied on staging first and checked through the storefront, checkout and admin before it’s released.
It closes known flaws, but attackers also try weak admin access, outdated extensions, injected checkout scripts and poor server configuration. That’s why patching comes with hardening, including a firewall such as Cloudflare in front of the store.
Not on its own. The store needs cleaning first: injected code and backdoors removed, then the flaw patched so the attacker can’t get back in the same way.
At that point the fix is an upgrade to a supported version, not another patch. We’ll plan it with you before it becomes urgent.
Adobe Commerce (Magento 2) services
Explore the Magento services Magebit has to offer.
Get a patch-status check
Tell us which store and version you run. We’ll show you what’s outstanding, what’s blocking it, and how we’d get you back on schedule.
- 1
We check your store
Patches outstanding and how long each has been open.
- 2
A ranked plan
What to clear first, and what’s blocking it.
- 3
Delivered your way
Through SOLVE, or inside a dedicated team.