Within just two to three months, they resolved issues that previously seemed unresolvable.
Tim Johnson
CTO
Every control treated as unproven until evidence says otherwise. Each item resolved to Pass or Fail against captured output, not opinion.

Adobe Commerce gold partner
#1 Adobe Commerce partner worldwide
Hyvä Platinum Partner
40+ projects delivered
ISO certification
9001 & 27001
Most certified Hyvä agency worldwide
200+ Adobe Commerce Certifications
Magento Association
Platinum Partner





Ransomware announces itself. A payment skimmer sits quietly in your checkout, taking card details for months while every metric looks normal.
 On a platform taking cards, that's the difference between a vulnerability and a data-loss event
It doesn't remove whoever is already inside. These four survive an upgrade untouched.
Most audits look for known issues. Ours assumes insecurity until evidence says otherwise.

Controls claimed present are re-verified live. Where documentation and platform disagree, the platform wins.

Access paths traced to effective permission, not intended. Role names resolved to what the holder can do.

Pass or Fail, supported by command output, a configuration export or an HTTP response.

Configuration reads, permission queries, static analysis. No changes, no exploitation attempted.

Shareable with a bank, partner or enterprise reviewer without editing.

Redacted from a real report. Verdicts are written so a non-technical reader can act.
29findings
7Passed
Findings by severity
| Area | Verdict | Finding |
|---|---|---|
| External perimeter | Holds | Edge-only ingress enforced at the network layer. Origin unreachable directly. |
| Administrative exposure | Inconsistent | Internal consoles address-gated; storefront admin reachable from anywhere. |
| Identity and access | At risk | Shared credential path, no per-person revocation, no attribution. |
| Detection and response | Largely absent | Rate limiting off, image scanning off, audit logging disabled. |
| Secret management | Sound | No credentials in the repository or in git history. |
| Workload hardening | Minimal | No segmentation, no admission policy, no container security context. |
Three layers, examined against your version, configuration and hosting.
Plus roles, file permissions, mail authentication and backups.
Plus DNS hygiene, secret storage and recovery testing.
Plus session integrity and access-log review.
A Magento estate is too large to examine by hand in the time anyone will pay for, so traditional audits sample. Sampling is how findings get missed.

Including the modules nobody documented and the one a contractor wrote in 2019.
Every modification surfaced, then classified as customization, forgotten patch or something else.
Obfuscated, encoded or split-across-files skimmers, caught by anomaly detection at file level.
Magento, extensions and every composer dependency against published CVEs, in minutes.
Millions of lines searched for exploitation attempts, public-path writes and login anomalies.
Every item read from live values rather than from documentation.

A CVE matching your version means nothing until someone establishes it's exploitable here.
A skimmer that looks like analytics, or an integration reported as a breach. Both calls are human.
Whether an account should exist, or an endpoint is deliberate. AI can't know, and guessing is worse.
Nobody hears they've been breached on the strength of a machine flag. Evidence is verified first.
Every finding carries a certified engineer's judgment. AI drafts, people are accountable.
Codebase, config, logs, dependencies and infrastructure state captured
Static analysis, dependency and CVE matching, integrity comparison
Every file read, patterns classified, candidates ranked by reachability
Exploitability on your configuration, severity, business context
No finding enters the report without a captured artefact behind it
400 signals
become around a dozen findings worth your attention. The reduction is the work.

Not into the report. Every finding must cite a captured artefact that anyone can re-check afterwards. A claim without an artefact never reaches you.

No. Client code and configuration are handled inside our ISO 27001 practice, under the same read-only, least-privilege, revoked-at-the-end rules as the rest of the audit.
Your code and data stay inside our ISO 27001 practice and are never used to train a model.
Not by a scanner's score. By reachability and blast radius on your configuration.
Where a finding is rated lower than it looks, the report says why, so you can disagree with the reasoning.
One document, written for the reader who won't open the detail and the one who will.
The section most audits leave out
Where the estate is sound, where the material risk sits, and what would move it.

Risk in commercial terms, audit goal, what was checked, and a validation table.

Sequenced work grouped by urgency and dependency, outage-risk items flagged.

What done looks like for each item, so completion is testable, not declared.

Who does each piece, and what we need from you, listed up front.

Recorded explicitly, so no area is presented as clean by omission.

What was used, how it was tested, and where the artefacts are retained.
Automated tooling is part of the audit, not the point of it.
A scanner reports61 dependencies out of date
The audit reports9 of those 61 are reachable from the storefront, the rest are dev dependencies
A scanner reports4 CVEs match your version
The audit reports1 CVE is exploitable on your configuration, and is being used in the wild
A scanner reportsA missing security header
The audit reportsThat header matters here because checkout loads three third-party scripts
A scanner reports400 findings sorted by CVSS
The audit reports11 findings that need action, in the order they should be done
Security work needs the access attackers want. All of it read-only.
 Least privilege, no changesISO 27001 certifiedNever published
Changes made to production. Every check is a configuration read, a permission query or static analysis.

Server configuration, file system and malware analysis

Configuration review, admin and token inventory

Configuration, extension inventory, cache and indexer status

Code review, version control settings, history secret scan

Execution rules in writable paths, TLS, exposed services

Edge WAF, rate limiting, TLS mode, headers, request logs
Exploitation attempts, cron history, incident timeline
Extension vulnerability and payment-flow review
Larger estates, multi-environment setups and complex hosting are scoped on the first call.

The full pass across application, infrastructure and compromise assessment, plus the report and roadmap.

Under our Fixed Cost Estimate Guarantee, so the approved number is the number you pay.

Around 10 hours against our standard checklist, each item marked Done or Failed, failures estimated.

Only once the findings show what's actually required, so nobody pays for a fix list written blind.
You don't need to suspect a breach. You need a reason to want certainty.
 Patches have been skipped and nobody can say which
 A partner or bank is asking security questionsFraud or chargebacks have moved
 You've inherited a store, or you're buying one
 Peak season is coming, when your team is busiestSomething looks wrong and you can't prove it
A skimmer steals card data every hour it runs. Our emergency line puts a certified developer on your store within an hour.
Findings are only worth the remediation behind them, and the cadence that stops the drift coming back.

Scoped after the report, with the approved estimate as the final price.

Under a support plan, Adobe's releases are applied on schedule.

The lighter checklist on a cadence, so drift gets caught while it's cheap.

File integrity, uptime and anomaly alerting, with 24/7 response behind it.

Kevin Hughes
European Technical Director
Within just two to three months, they resolved issues that previously seemed unresolvable.
Tim Johnson
CTO

There is no challenge for which they can't find a solution.
Will Aubuchon
CEO

What I value most is consistency. Magebit knows our store inside out, responds fast, and keeps it running smoothly year after year.
Marian Gaidoš
CEO

The top-ranked Adobe Commerce agency on the planet by Adobe themselves.


The most certified Hyvä agency in the world. Confirmed by Hyvä themselves, twice.
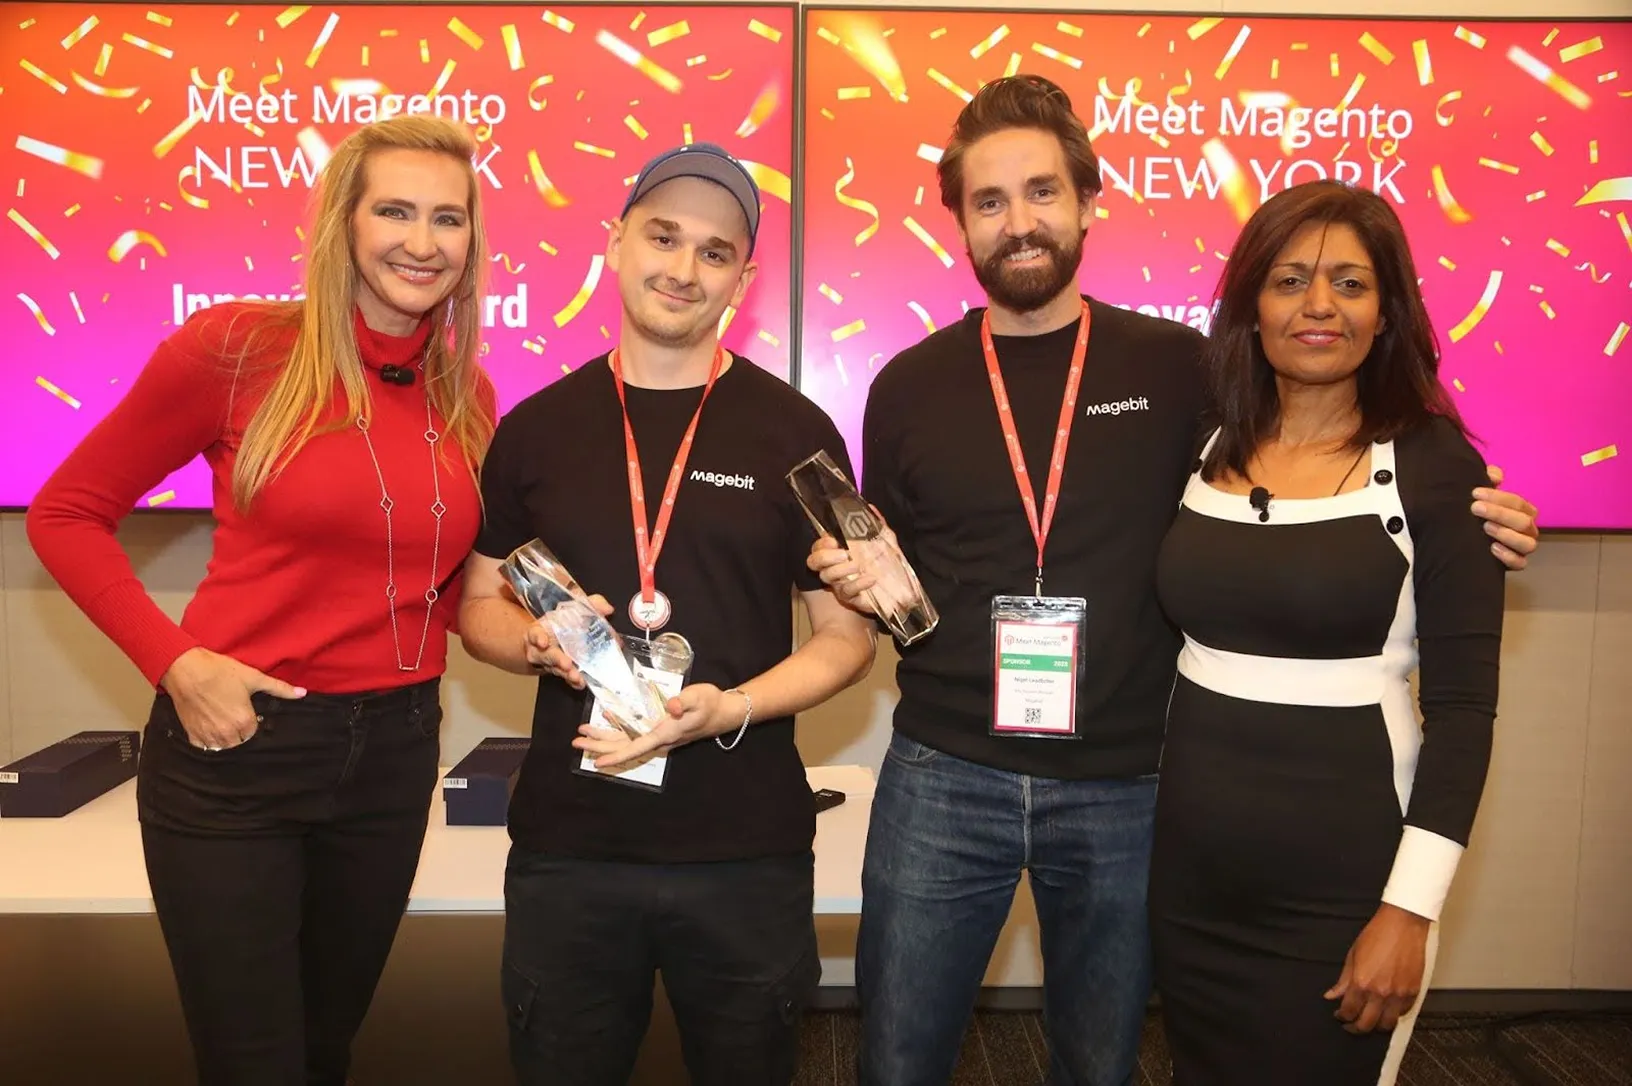
Innovator, World Traveler, and eCommerce Excellence awards across Meet Magento NYC and HIVE London, and more.
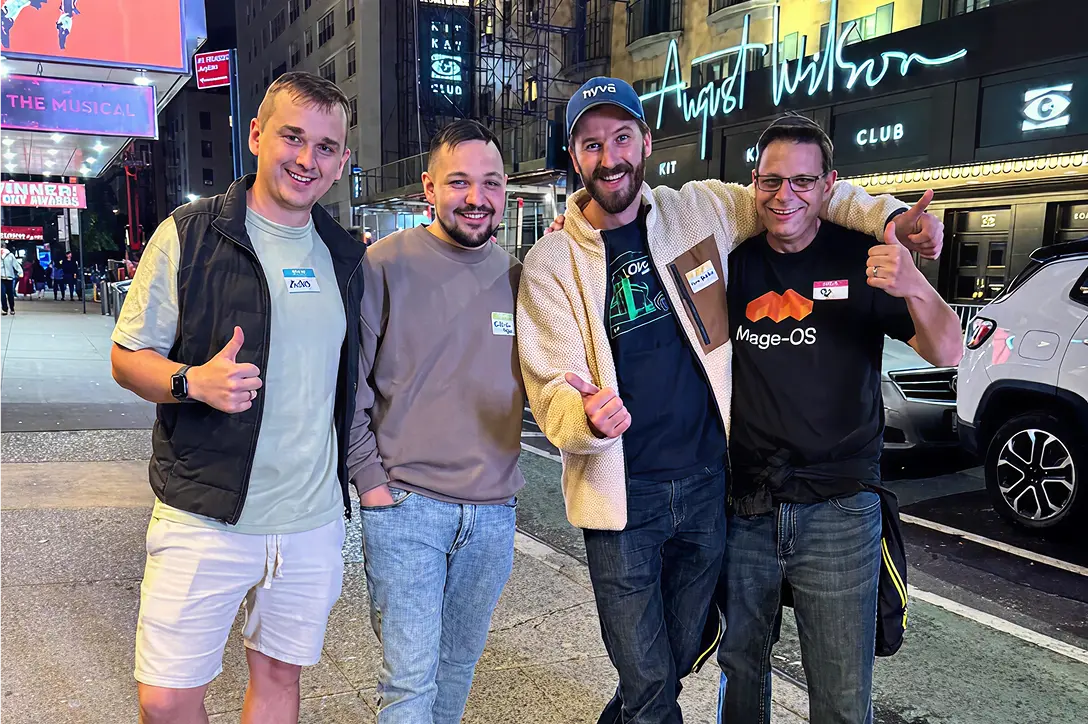
The most-certified Hyvä agency worldwide and the first Hyvä Platinum Partner in the USA. 55+ certified developers and 40+ projects delivered.
ISO 9001 & 27001 for quality and security.
Truly agile team that moves and adapts faster than your typical agency.
UX grounded in large-scale ecommerce research.
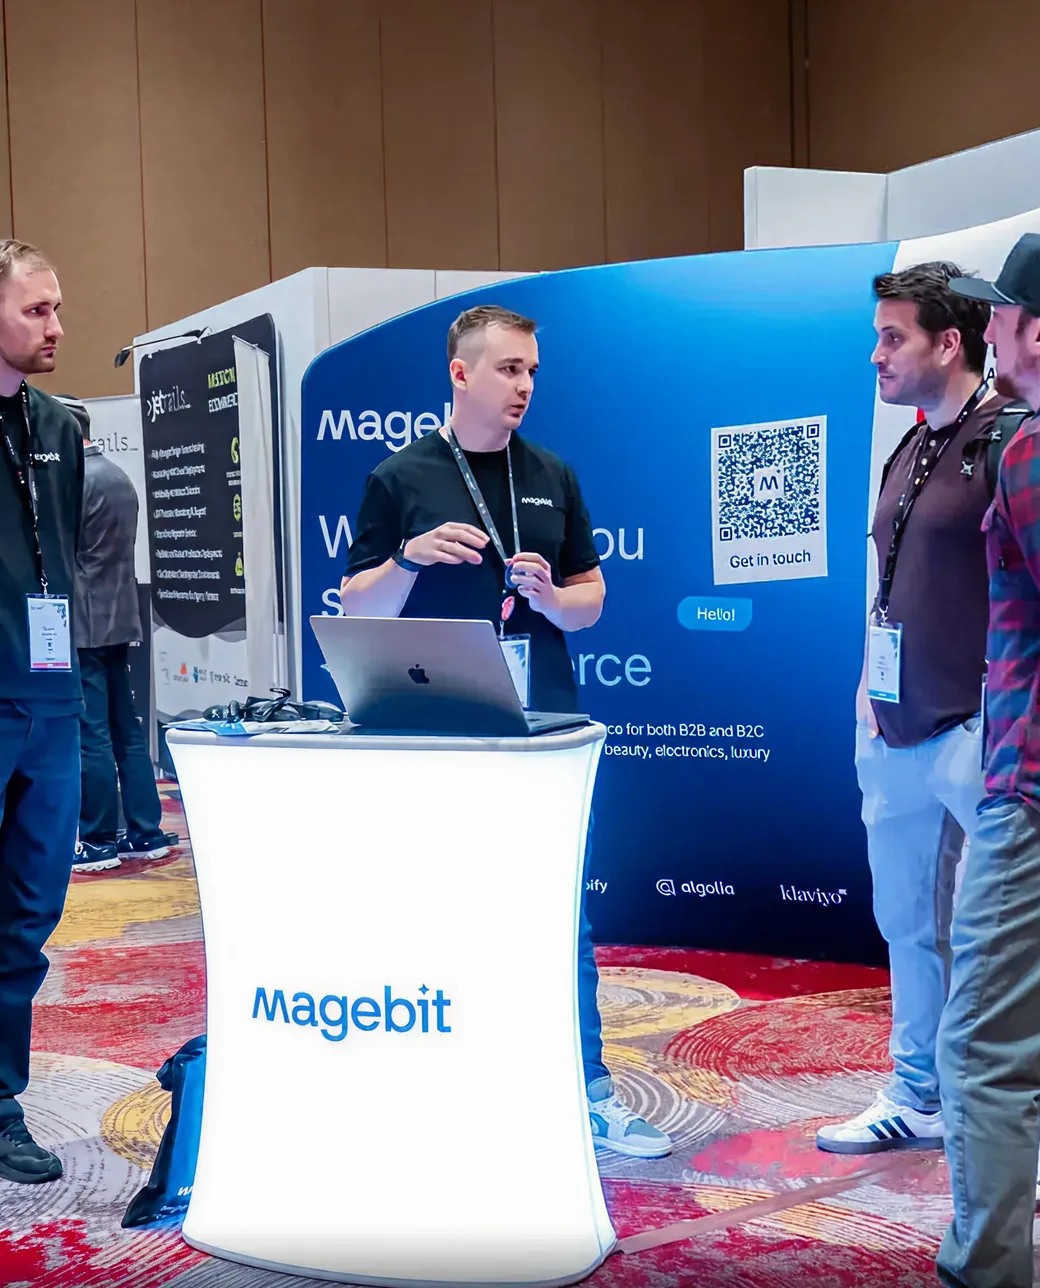
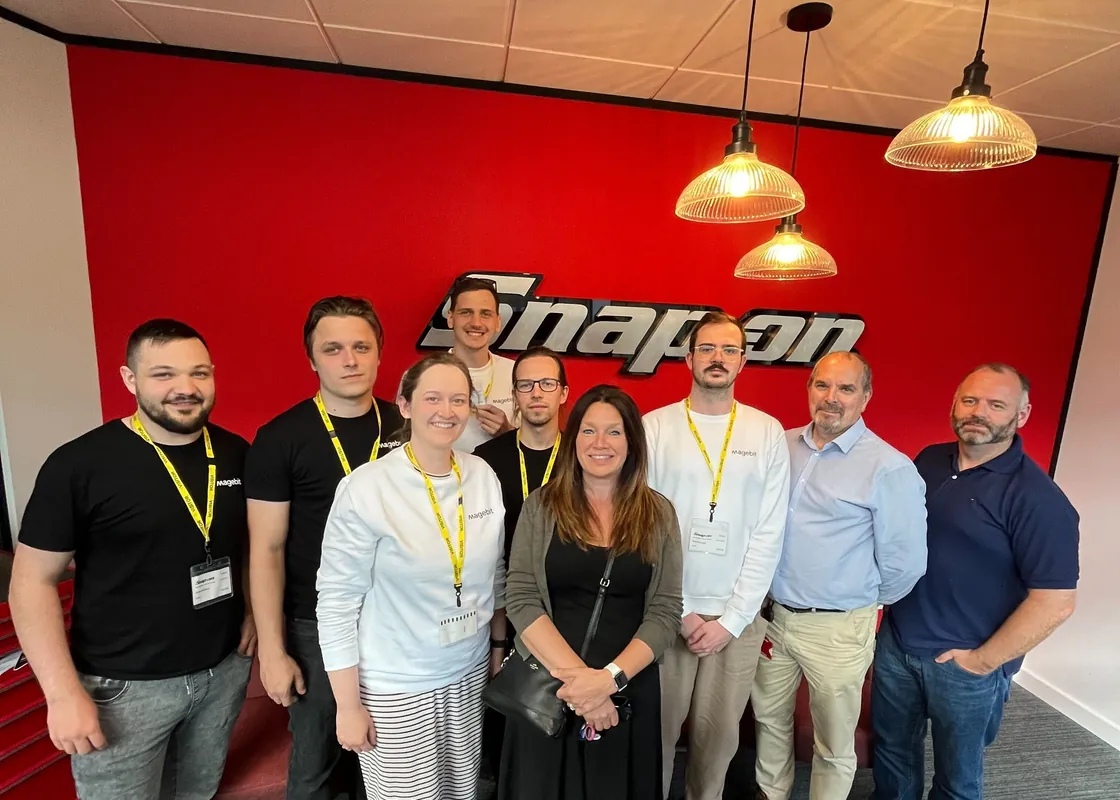
Magebit team at Meet Magento, #1 Adobe Commerce agency worldwide.
By certified developers, Magebit holds the number-one spot among Adobe Commerce agencies worldwide, and we’re the most certified Hyvä agency on the planet. Proof that the depth is real, not a logo on a page.
#1 Adobe agency worldwide
200+ Adobe certifications
#1 Most certified Hyvä agency
Adobe Subject Matter Expert
Most reviews check configuration and stop. The question that matters is whether anyone is already inside.
Compromise assessment included
Webshells, skimmers, rogue admins, stolen tokens
Every control resolved to Pass or Fail
No third state, nothing assumed clean
Varies
Severity by reachability, not CVSS
Critical findings raised the same day
Sometimes
Findings against your own agency
Shareable with a bank or enterprise reviewer
Sometimes
ISO 27001 practice behind the handling
Sometimes
Every serious breach I've seen started as something small nobody had time to check. An audit is a week of attention against a problem that otherwise gets found by your payment processor. Tell me what you're running and we'll look properly.
Reviewed by Kristaps Rjabovs
Co-founder of Magebit, Forbes 30 Under 30
If you can't find the answer you're looking for, feel free to reach out to us. We're here to help.
A standard assessment is around 40 hours across application, infrastructure and compromise assessment, quoted as a fixed price before anything starts. Larger estates and complex hosting are scoped on the first call, and a lighter quarterly check against our standard checklist runs at roughly 10 hours. Remediation is always quoted separately, once the findings show what's genuinely required.
Compromise assessment is a core part of the audit: webshell and malware scanning, file integrity, skimmer detection in checkout templates, token and admin review, log analysis and persistence checks. If we find evidence, you'll know the same day, before the document exists.
It's designed to. Agency-side gaps in process, access management or implementation are recorded as valid failures and go into your roadmap like anything else. A typical report contains several. An audit that can't fail its own author isn't worth commissioning.
No. This assesses your application, configuration, access, infrastructure and whether the platform has already been compromised, all read-only and non-destructive. It describes reachable capability rather than demonstrated exploitation. If a pen test is what your situation calls for, we'll say so.
Largely. Hardening, edge protection, execution rules and monitoring reduce exposure substantially, and the report states which target release closes each outstanding advisory, so the upgrade decision is made with real numbers.
AI does the volume work, reading every custom module rather than a sample, comparing your core against the official release, mapping versions and extensions to published CVEs, and searching a month of logs. A certified engineer then decides exploitability, severity and business context, and no finding enters the report without a captured evidence artefact behind it. Your code and configuration stay inside our ISO 27001 practice and are never used to train a model.
None. Every check is a read-only query, a configuration inspection or static analysis. Remediation only happens if and when you commission it separately.
Explore the Magento services Magebit has to offer.
Your version, your extensions, your hosting. You'll get findings that stand up to outside scrutiny, and a roadmap priced to close them.
Not a sales script.
Not held for the report.
The findings are yours to keep.
We use cookies.
Some help us see how the site is used and measure our ads. You choose — until you do, no cookies are set and Google receives only cookieless signals that don't identify you. Privacy Policy